
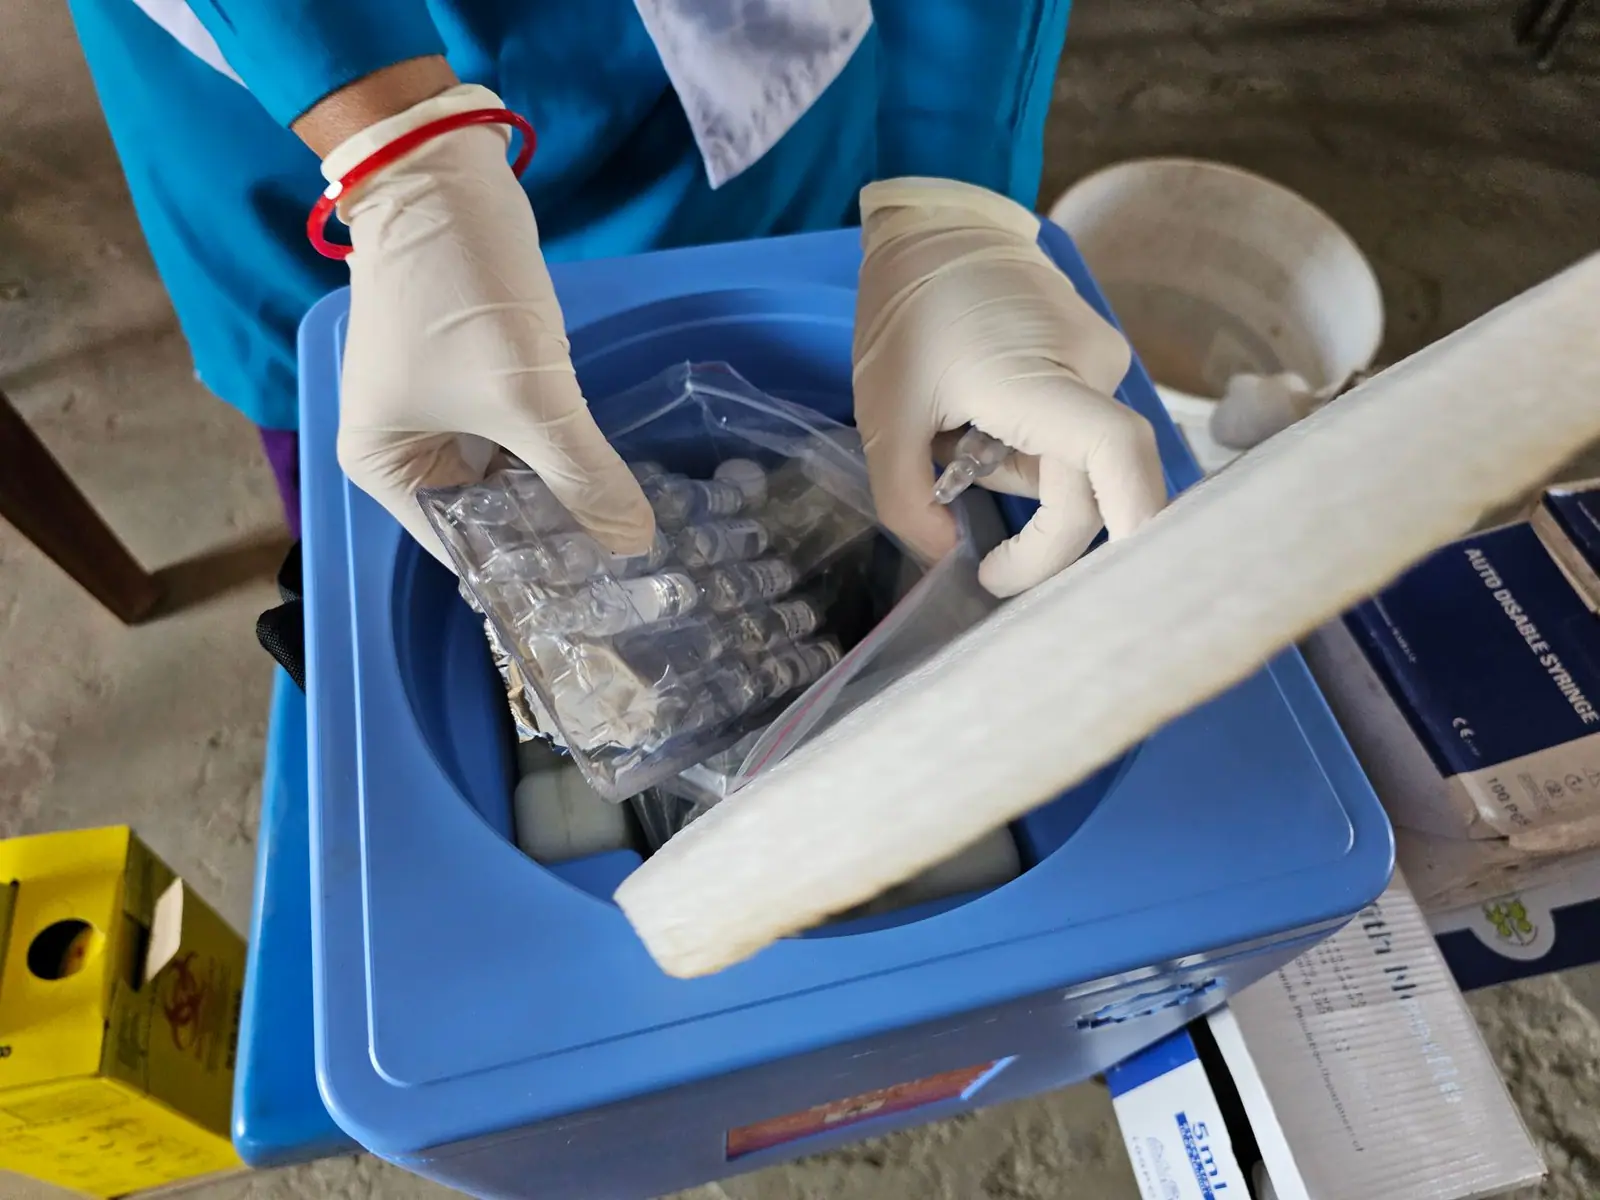
Hackers broke into the refrigeration units of France's blood service, EFS (Établissement Français du Sang), and changed the set temperature from minus 30C to 110C. A technician on duty reacted in time and the stocks were saved, EFS management confirmed.
The attack happened on the night of 2 November but only became known on 3 November.
The hackers got in through Coolworld, the firm that maintains EFS's refrigeration equipment. The units hold blood and plasma for transfusions. France's health ministry says about 1 million patients a year are treated with these stocks.
The technician saw the sudden change on the monitors and triggered the emergency protocol. Staff quickly moved all bags from the affected units to a safe place. EFS said it lost neither equipment nor blood products.
It is not clear who is behind the sabotage, or how many sites in France were hit in total.
EFS's cooling systems are connected to the internet. This lets staff monitor them remotely, but it often gives cybercriminals a way in too. Hackers also recently attacked the cold storage units of big supermarket chains in Europe, and an IT breach has already caused direct losses of money and goods.
Senior IT consultant George Cherin said internet-connected devices are being installed more and more often because they let people monitor and control buildings and machines from a distance. Without strict security rules, he said, they pose big risks to daily operations.
Cherin said the main problem is not that goods may spoil. A poorly protected device becomes a front door to a company's central network. If the network is not split into separate parts, attackers use such a sensor as a foothold and move on to other systems. A small breach in one sensor can give them direct access to payment terminals, financial systems and databases. From there they can leak sensitive data or launch ransomware that halts all trading.
Many such devices are installed without the most basic security settings. They keep their factory passwords, run over unprotected network links or have built-in software with known weaknesses. This software is often hard to update with regular patches, and sometimes cannot be updated at all.
Omar Benbouazza, co-founder of RootedCON, believes that reliance on modern technology could prove very costly. He said artificial intelligence tools make life easier for attackers and cut the time needed to prepare an attack from several months to a few minutes.
Comments (0)
No comments yet.